On the 31st August I got an email from a customer, telling me that they had found an imitation of my data wrangling software on Github. I’m not linking to it, but here is a screenshot:
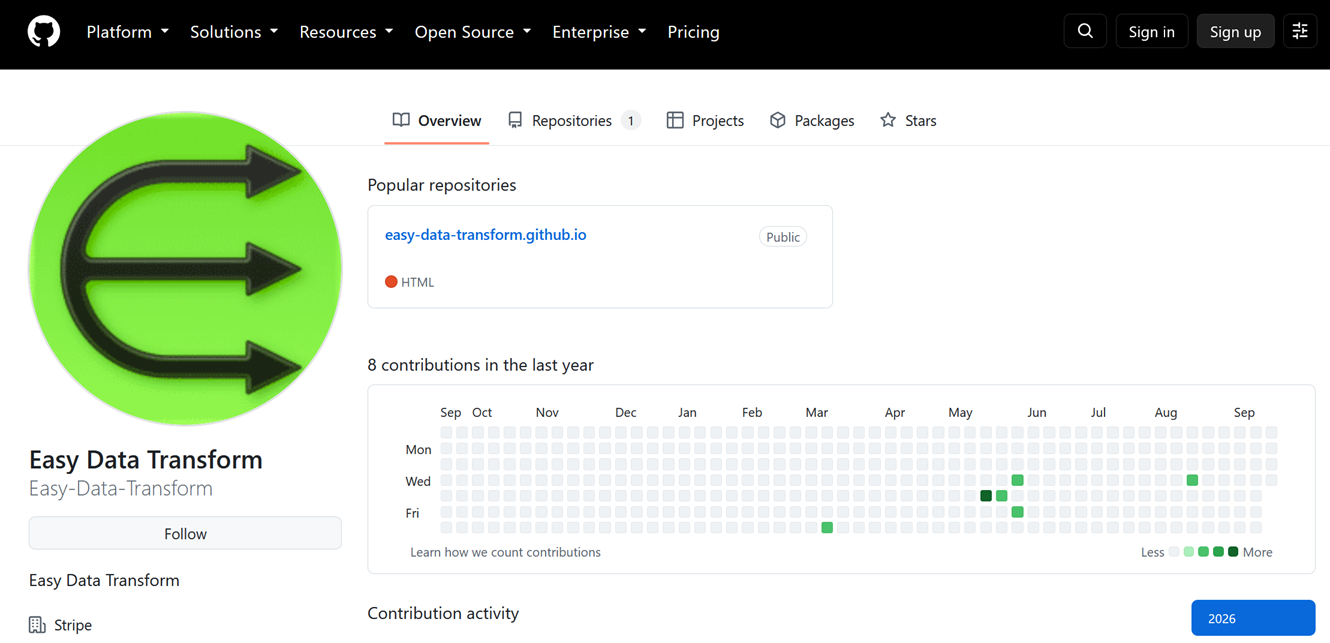
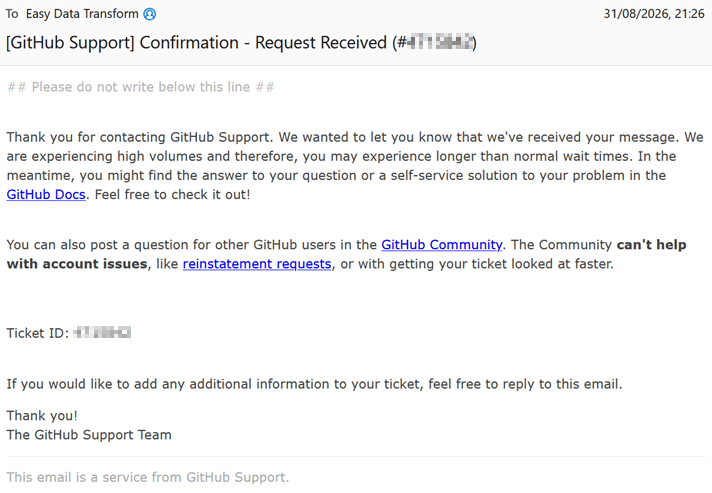
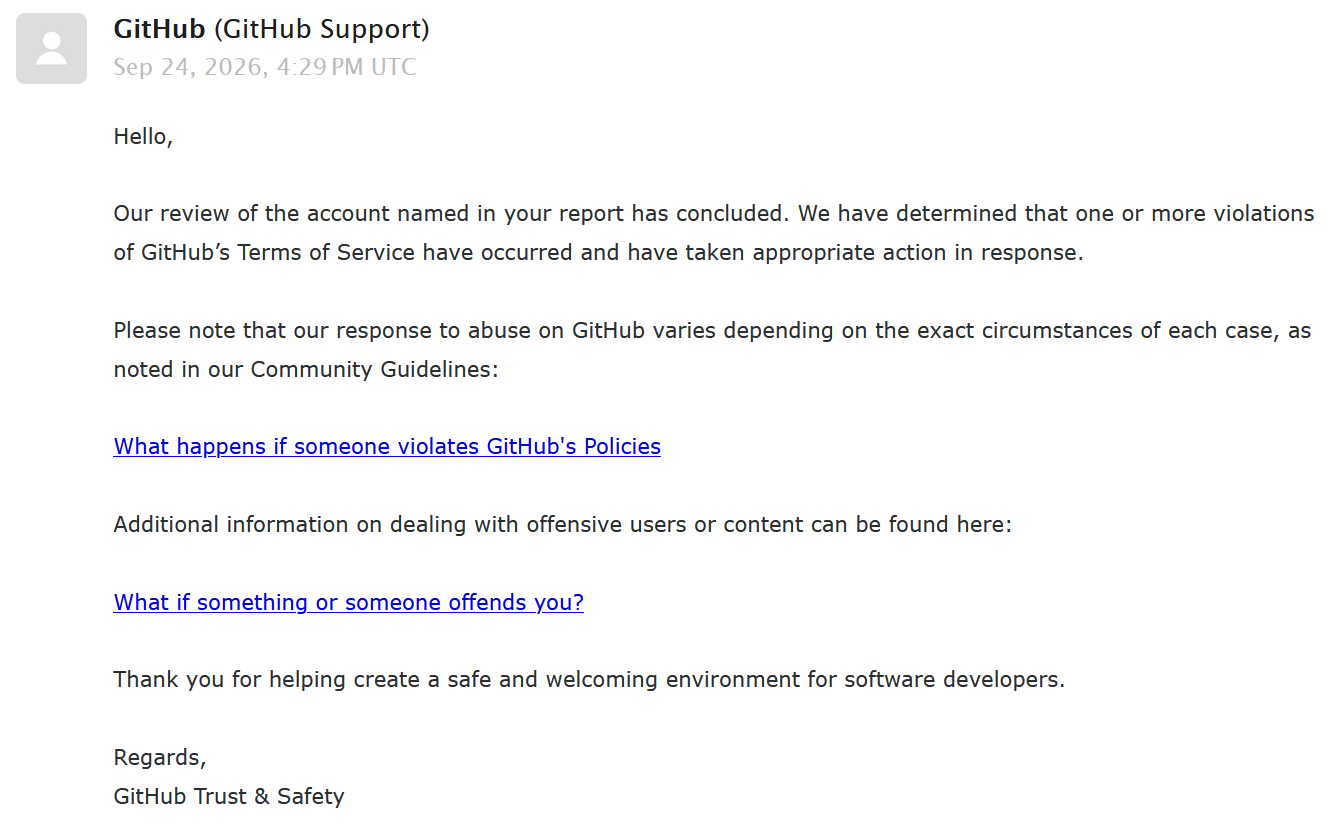
It is using our product name and logo, without permission. I reported it to Github as an imitation on the same day. I got this reply:
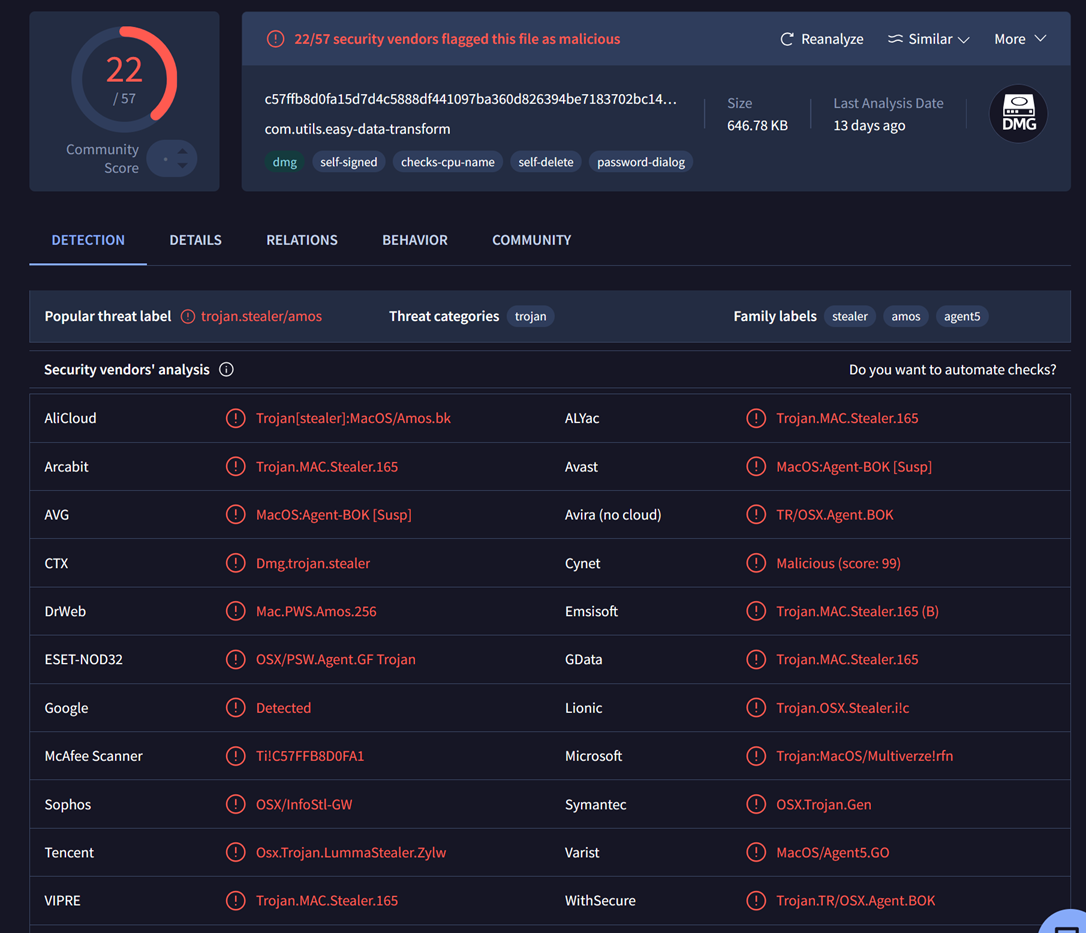
A colleague scanned the Mac .dmg file from the repository using virustotal.com and got a whole load of malware warnings:
Using data recovery software Isobuster he found out that they have also changed the background image of the .dmg:
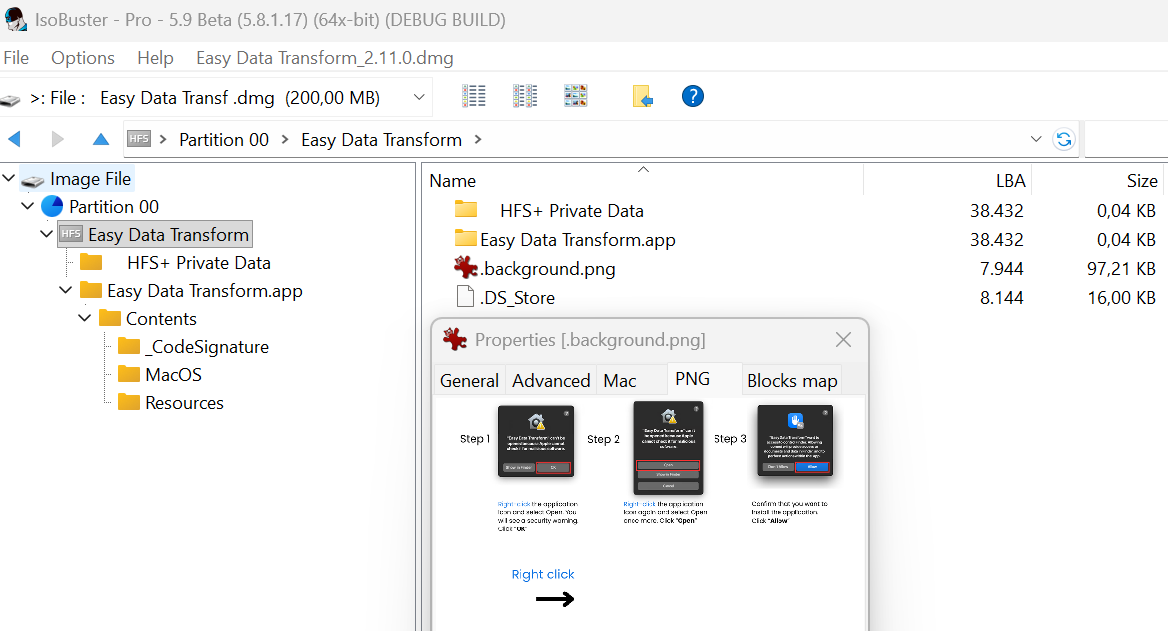
The new image encourages downloaders to ignore any warnings about the malware!
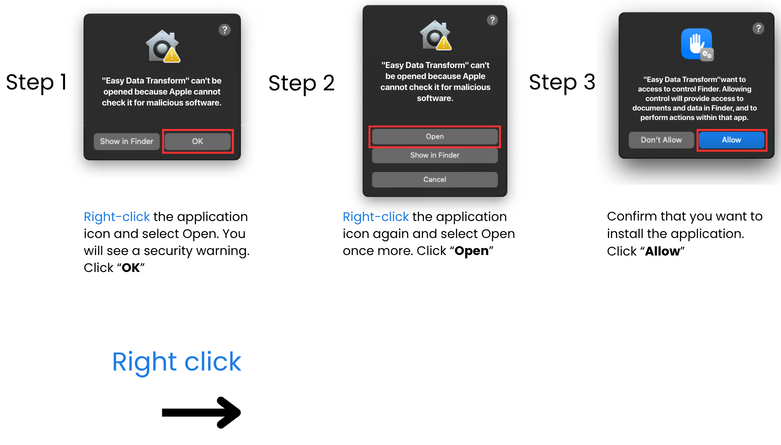
I reported this additional information on the 10th September.
As of the 23rd September, I have had no response from Github support beyond the original automated email. 23 days without a reponse. This is pisspoor. Do better Github.
I’m not sure what my next line of attack is. A DCMA takedown request to Github?
Realistically the only people likely to download the .dmg are those trying to avoid paying for a license for Easy Data Transform. I don’t have a huge amount of sympathy for them if they get their computers compromised. But I really don’t like bad guys taking advantage of my hard work.
Ps/ Always download software from the vendor, where possible.
** Update 24-Sep-2026 **
Github finally took the offending page down approximately 10 minutes after this post appeared on the front page of Hacker News. Total coincidence. I’m sure!
Moral of the story. If you want even the most basic level of support from Github, you need to get on the front page of Hacker News.
And it seems they are able to do things very quickly, when they want to.


looks like GH has actioned on it!
10 minutes after it made the front page of HN. What a massive coincidence…
The same thing happened to us.
We reported the issue to GitHub back in June. An acknowledgement arrived immediately but we haven’t had a peep since then. Thankfully the folks at TinyURL moved quickly to disarm the virus-ridden download and protect our users.
I’m very disappointed in GitHub. It should take all of 5 seconds to determine that the site is fraudulent. Yet it remains up, causing confusion for customers searching for our product in Google (it’s link #2). Maybe GitHub doesn’t care?
They seem to care if you get front page of Hacker News!
Perhaps you should try a DCMA takedown request?
At your suggestion, I submitted a DCMA takedown request. GitHub responded three days later by nudging me to submit a “Trademark Violation” report so I completed that as well. And lo and behold, just a few hours later, the page was finally taken down!
Many thanks for your article. Without it, I’d still be waiting to her back from the “Report Abuse” ticket I submitted back in June. Clearly that process is severely understaffed, or outright broken.
Result!
Ah, I found this and wrote about it months ago. Very upsetting to see nothing has changed.
https://brennan.day/the-curious-case-of-the-triton-malware-fork/
It’s important to use the correct form when reporting these issues to GitHub. These are legal issues that the normal support staff likely isn’t allowed to handle. When (hacked) copies of your actual software are posted, send a DMCA takedown notice. When a repository uses the name of your product without copying your actual software, send a trademark policy violation report. Use the specific form on GitHub’s website. I’ve had multiple repositories taken down for trademark infringement. When the repository was obviously bogus, it got taken down in a few days. In one case where the app itself was legitimate except for the trademark infringement, it took a few weeks and some follow-up emails. GitHub gave the other side time to respond. But when they didn’t, the repository was taken down.
DCMA might well have got a faster response. But it is quite poor that reporting an imitation (followed by additional information on it being malware) didn’t get a response until it appeared on HN.
I’m not sure if this is something you’d consider doing, but if it happens again in the future, perhaps offer one-year licences for free while you’re getting the fake copies taken down, or give a free licence to anyone who reports an imitation copy.
That way, you not only undermine the scammers’ plans, but you may also gain genuine paying customers when those free licences expire.
It’s also worth thinking about the people who download the fake version without knowing what they’re doing and end up with an infected computer. You can already imagine what they’ll write online: “I downloaded data wrangling software and it had malware.”
Even though the malware came from a fake copy, the damage to the real product’s reputation could already have been done.
As for GitHub, I reported someone who was teaching young people how to get around the UK age restrictions
>offer one-year licences for free while you’re getting the fake copies taken down
I won’t be doing that.
>give a free licence to anyone who reports an imitation copy
That creates an incentive for people to create imitations.
>It’s also worth thinking about the people who download the fake version without knowing what they’re doing
I doubt anyone going to that repository is thinking it is a genuine download.